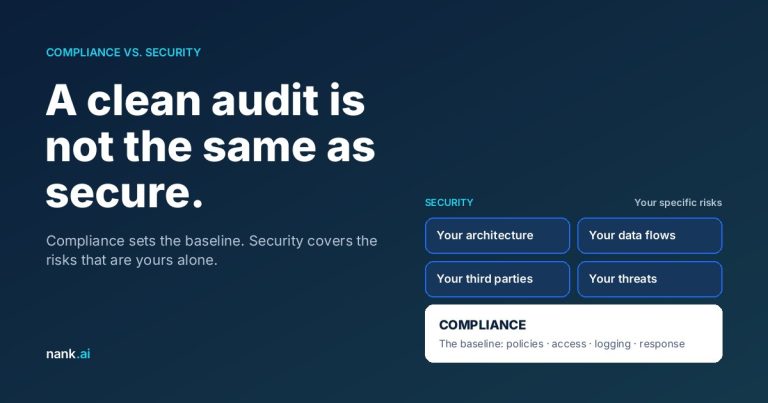
Compliance vs. Security: Why a Clean Audit Does Not Make You Secure
Compliance gives you a baseline of controls. Security covers the risks that come from your own systems, data and business. Where audits stop, and how you

Practical writing on SOC 2, ISO 27001 and the privacy law Canadian companies actually have to follow. We are a Toronto compliance firm, and this is where we explain the work: what a report costs, how long an audit really takes, and what an auditor asks for. Start with our Compliance as a Service overview, or go straight to the compliance library.

Compliance gives you a baseline of controls. Security covers the risks that come from your own systems, data and business. Where audits stop, and how you
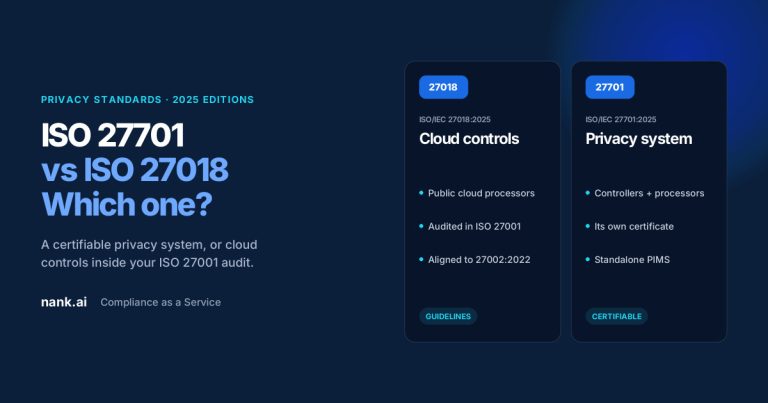
ISO 27701:2025 is a certifiable privacy management system. ISO 27018:2025 is guidance for public cloud PII processors, audited inside ISO 27001. What each covers and which

Four challenges the common compliance platform creates for the teams that use it, what each one costs, and what to ask a vendor before you sign.
Compliance-as-a-Service moves most of the SOC 2 work to a platform and a named manager. Four things stay with you, and here is why.

TL;DR Compliance automation software shows you what is wrong. It cannot write your policies, run your internal audit, or sit across from an auditor when they
OWASP, PTES, NIST and OSSTMM compared. Which methodology fits your scope, and what an auditor expects to see in the report.
Most of what we write here comes out of engagements with Canadian and U.S. companies. Buyers ask for the same two reports again and again. Our SOC2 service engagements answer the first. Our ISO 27001 certification engagements answer the second. Alongside them sit obligations that most companies gloss over: PIPEDA federally, PHIPA for health information in Ontario, Law 25 in Quebec, and OSFI expectations for federally regulated financial institutions.
Our compliance services engagements account for all of that from the first conversation. One control library covers the framework you are certifying against and the privacy law you already follow.
Data residency compliance is a standing condition in public sector and healthcare contracts, and a growing one in enterprise procurement. Your evidence, policies and control records stay in your country, so the answer to that questionnaire question is short and provable.
Readiness, control design, evidence and auditor coordination for the Trust Services Criteria. Buyers write it SOC2 or SOC 2. Same report.
Scoping, Statement of Applicability, risk assessment and internal audit, through Stage 1 and Stage 2 with an accredited certification body.
PIPEDA, PHIPA and GDPR advice, security program design and penetration testing coordination for teams without a CISO.
New here? The compliance platform shows how the controls, evidence and audits fit together, and about Nank.ai explains why we built it the way we did.
Tell us which framework your buyers are asking for and what you have in place today. We will tell you what the program looks like and how long it takes. A real compliance manager on the call, no obligation.
We use cookies to improve your experience on our site. By using our site, you consent to cookies.
Manage your cookie preferences below:
Essential cookies enable basic functions and are necessary for the proper function of the website.
These cookies are needed for adding comments on this website.
Statistics cookies collect information anonymously. This information helps us understand how visitors use our website.
Google Analytics
Service URL: www.nank.ai (opens in a new window)
You can find more information in our Cookie Policy and Privacy Policy.