
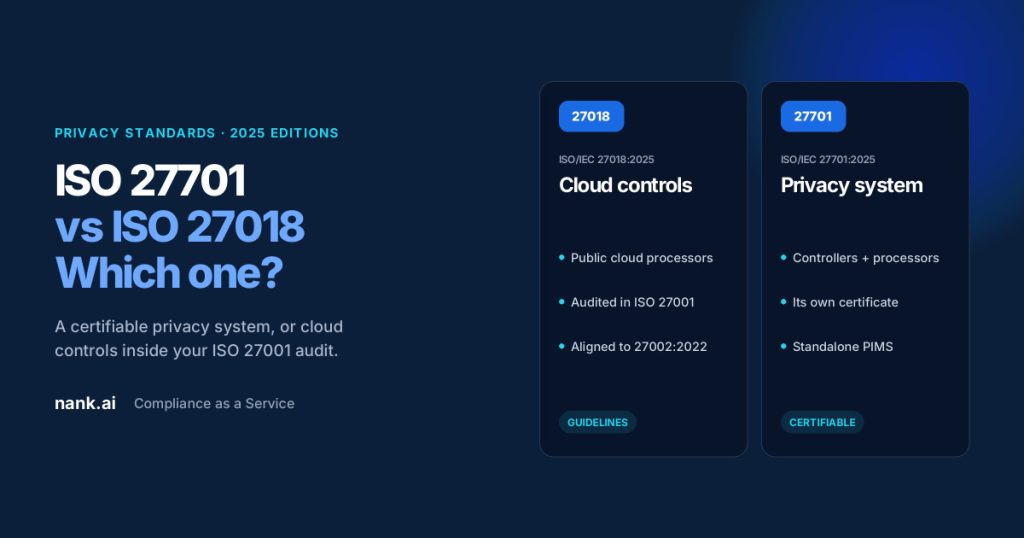
ISO 27701 · ISO 27018 · Cloud privacy
Both standards protect personal data, and both got a new edition in 2025. They are not two versions of one idea. One is a certifiable privacy management system. The other is a set of cloud controls that lives inside your ISO 27001 audit.
TL;DR
ISO/IEC 27701:2025 is a privacy management system you can certify on its own. ISO/IEC 27018:2025 is guidance for public cloud providers that process personal data for customers.
- Scope. 27701 covers PII controllers and PII processors in any setting. 27018 covers one role, the public cloud PII processor.
- Certification. 27701 has its own certificate. Auditors assess 27018 as part of an ISO 27001 audit, not on its own.
- What changed in 2025. 27701 became a standalone standard. 27018 now follows the ISO 27002:2022 control set and adds a table back to its 2019 edition.
- How they connect. Annex E of 27701 maps its controls to 27018, so you can run both from one control set.
If you already hold ISO 27001 and sell a public cloud service, 27018 is the smaller step. If buyers want a privacy certificate, or you act as a controller too, you need 27701.
Sources: ISO/IEC 27018:2025 · ISO/IEC 27701:2025 · UKAS transition bulletin
Two standards, two kinds of document
People compare these two as if you pick one. That is the first mistake. They answer different questions.
ISO/IEC 27701 answers “how do we run privacy as a managed system?” It sets requirements for a privacy information management system (PIMS). It has clauses you must meet, an Annex A of controls, and a certificate at the end. The 2025 edition, published on 14 October 2025, made it a standalone standard. You no longer need ISO 27001 to use it.
ISO/IEC 27018 answers “which controls protect customer data in a public cloud?” It gives control objectives, controls and guidance for one kind of firm. That firm runs a public cloud service and processes personal data under contract for its customers. The third edition came out in August 2025 and replaces the 2019 edition.
The 2025 title makes the point. The 2019 edition called itself a code of practice. The 2025 edition calls itself guidelines. Neither is a management system standard, and neither sets requirements you can certify against alone.
Cloud controls
Guidance for public cloud PII processors, used inside an ISO 27001 ISMS.
A privacy management system
Certifiable on its own, for controllers and processors.
How the two 2025 editions are built, and where they meet. Clause and annex names follow the published standards.
Who each standard is for
ISO 27018 fits one role in one setting
ISO 27018 applies to firms of any size that process PII as processors, through cloud computing, under contract to other firms. Most multi-tenant SaaS, PaaS and IaaS vendors fit that description for the customer data they host.
The standard says its guidance “can also be relevant” to controllers. It stops there. It does not tell a controller how to meet its own duties. Consent and notice to the people whose data you collect sit outside it.
ISO 27701 covers both roles, in any setting
ISO 27701 applies to any firm that handles PII, cloud or not. It covers both roles. Table A.1 holds the controller controls and Table A.2 holds the processor controls. You apply the tables that match what you do.
This matters more than it looks. A SaaS vendor is a processor for the data its customers load. It is also a controller for its own staff records, its sales leads and its user accounts. ISO 27018 speaks to the first role only. ISO 27701 speaks to both.
What trips people up
A 27018 claim does not tell a buyer how you handle your own personal data. It tells them how you handle theirs, in your cloud. If a customer’s privacy team asks how you run privacy across the whole firm, 27018 is not the answer. That question points to 27701.
How you get audited
This is where the two part ways in practice.
ISO 27701 has its own certificate
An accredited certification body audits your PIMS against Clauses 4 to 10 and the Annex A controls you apply. ISO/IEC 27706:2025 sets the rules for those bodies. In Canada, the Standards Council of Canada accredits PIMS certification bodies. In the United States, ANAB does. Since 2025, you can hold a 27701 certificate with no ISO 27001 certificate beside it.
ISO 27018 rides on ISO 27001
ISO 27018 says you use it to pick controls when you build a cloud ISMS “based on ISO/IEC 27001”. Certification bodies treat it that way.
“ISO/IEC 27018 is a code of practice and is typically audited as an extension of ISO/IEC 27001.”
Linford & CoISO/IEC 27018 cloud privacy guide
In practice, you add the 27018 controls to your Statement of Applicability and your auditor tests them during your ISO 27001 audit. SGS, a certification body, says the 27018 audit can run with the ISO 27001 certification audit or after it. Either way, the ISO 27001 certificate comes first.
That leads to a point most comparisons skip. The 2025 edition of 27701 dropped its need for ISO 27001. The 2025 edition of 27018 did not. If you plan a standalone 27701 certificate with no ISMS, you lose the usual route to a 27018 claim. You can still use 27018 as guidance. You just cannot point to an audit of it.
What changed in each 2025 edition
ISO 27018:2025, a realignment
The foreword of the 2025 edition lists two main changes. ISO aligned the text with ISO/IEC 27002:2022, and added Annex B.
The first change is the big one. ISO 27002:2022 reorganized its 93 controls into four themes. Clauses 5 to 8 of ISO 27018 now follow those themes: organizational, people, physical and technological controls. Where a 27002 control needs no cloud PII guidance, 27018 just points to it. Where it does, 27018 adds guidance for the public cloud processor.
The second change is modest. Annex B is a table between the 2025 and 2019 control layouts. Open it first if your Statement of Applicability still cites 2019 control numbers. Annex A is still the heart of the standard. It holds the extra controls for public cloud PII processors, laid out by the privacy principles of ISO/IEC 29100.
ISO 27701:2025, a rebuild
ISO 27701 changed far more. The 2019 edition extended ISO 27001 and ISO 27002. The 2025 edition stands alone, with its own Clauses 4 to 10 and a new Annex A. Table A.3 brings the security controls a PIMS needs into the privacy standard itself. Annex B now holds the guidance for each Annex A control. Certificates issued against the 2019 edition must move to the 2025 edition by 31 October 2028. Our article on ISO 27701:2025 vs 2019 covers that change in detail.
Check your sources on Annex B
Some summaries describe the new Annex B in ISO 27018 as extra guidance. The standard’s own contents page calls it a correspondence with the 2019 edition. And in ISO 27701:2025, Annex B means something else again: guidance for the Annex A controls. Cite the standard and the edition, not just the annex letter.
Where the controls overlap
The overlap sits in the processor controls. ISO 27018 Annex A and ISO 27701 Table A.2 cover much of the same ground. Linford & Co lists the kind of topics 27018 adds for cloud processors:
- processing PII only as the customer instructs
- no use of customer PII for marketing or advertising without consent
- returning or deleting PII when the contract ends
- telling customers about subcontractors and where PII may be processed
- logging access to PII
- telling customers about a breach that involves their PII
ISO 27701 treats the same duties in Table A.2 and in the security controls of Table A.3. Annex E of ISO 27701 maps its controls to ISO 27018 and ISO/IEC 29151. So you do not need two control sets. You build one, and use Annex E to show coverage of both.
Neither standard maps to North American law. ISO 27701 maps to the EU GDPR in Annex D. Your customers may need you to cover PIPEDA or Quebec Law 25 in Canada. They may need HIPAA and the state privacy statutes in the United States. Either way, you build that map yourself.
| Topic | ISO/IEC 27018:2025 | ISO/IEC 27701:2025 |
|---|---|---|
| Type of document | Guidelines, a code of practice | Management system standard |
| Certifiable alone | No. Audited within ISO 27001 | Yes |
| Roles covered | PII processor | PII controller and PII processor |
| Setting | Public cloud services | Any setting |
| Builds on | ISO 27001 and ISO 27002:2022 | Stands alone, can integrate with ISO 27001 |
| Controls | Guidance on 27002 controls, plus Annex A | Annex A Tables A.1, A.2 and A.3 |
| Main 2025 change | Aligned with ISO 27002:2022, Annex B added | Became standalone, new Annex A |
| Mapping | None to 27701 | Annex E maps to 27018 and 29151 |
| Transition deadline | Set by your certification body | 31 October 2028 for 2019 certificates |
Which one you need
Start from what you sell and what your buyers ask for.
You hold ISO 27001 and run a public cloud service
Add ISO 27018. It adds controls to your Statement of Applicability, and your next ISO 27001 audit covers them. This is the smallest step.
Buyers want a privacy certificate
Build a PIMS to ISO 27701:2025. Run it with your ISMS as one integrated system, and use Annex E to cover ISO 27018 at the same time.
You have no ISMS today
ISO 27701 alone is now an option. ISO 27018 still needs ISO 27001 before an auditor will test it. Pick based on which certificate your buyers ask for.
When to hold both
Many cloud vendors will end up with both, and it costs less than it sounds. The ISMS gives you the security base and the 27018 audit route. The PIMS gives you a privacy certificate that covers your controller role too. One risk method, one internal audit and one management review can serve both, as long as your records show each system got covered.
What good looks like
One control set that traces to ISO 27001 Annex A, ISO 27018 Annex A and ISO 27701 Tables A.1 to A.3. A Statement of Applicability that cites 2025 control numbers only. A clear record of where you act as a controller and where you act as a processor. And a map to the privacy laws your customers care about, in Canada and the United States.
What to do next
- Name your roles. List the PII you handle as a controller and the PII you handle as a processor. That list decides which 27701 tables apply, and whether 27018 fits at all.
- Ask your buyers. Check which certificate their security reviews ask for. Some name 27018. Others ask for a privacy certificate, which means 27701.
- Update to the 2025 editions. Use Annex B of 27018 and Annex F of 27701 to move 2019 control numbers to their 2025 homes.
- Build one control set. Use Annex E of 27701 to trace each control to 27018, so one piece of evidence serves both.
- Talk to your certification body. Confirm when it can audit each 2025 edition, and whether it can combine the audits in one visit.
For the basics of the privacy standard, see what ISO 27701 certification is. To build the system, our guide to designing and implementing a PIMS walks through each step. For the ISMS underneath 27018, start with our complete ISO 27001 guide.
Frequently asked questions
What is the difference between ISO 27701 and ISO 27018?
ISO 27701 is a privacy management system standard that you can certify on its own. It covers PII controllers and processors in any setting. ISO 27018 is guidance for public cloud providers that process PII for customers. Auditors assess it as part of an ISO 27001 audit.
Can you get certified to ISO 27018?
Not on its own. ISO 27018 is a set of guidelines, not a management system standard. Certification bodies audit its controls as an extension of ISO 27001, during or after the ISO 27001 certification audit.
Does ISO 27701:2025 replace ISO 27018?
No. Both are current, and ISO published a new edition of each in 2025. Annex E of ISO 27701 maps its controls to ISO 27018, so you can run both from one control set.
What changed in ISO 27018:2025?
The foreword names two main changes. ISO aligned the text with ISO/IEC 27002:2022, and added Annex B, a table between the 2025 and 2019 control layouts. The title also changed from a code of practice to guidelines.
Do I need ISO 27001 to use ISO 27018?
You can read and apply ISO 27018 as guidance without it. To have an auditor test your 27018 controls, you need an ISO 27001 ISMS, since certification bodies audit 27018 as part of it.
Which standard should a SaaS company choose?
If you hold ISO 27001 and host customer PII in a multi-tenant cloud, ISO 27018 is the smaller step. If buyers want a privacy certificate, or you need to cover your controller role, choose ISO 27701:2025. Many SaaS firms hold both.
Key takeaways
- ISO 27701:2025 is a certifiable privacy management system. ISO 27018:2025 is a set of cloud privacy guidelines.
- 27701 covers controllers and processors in any setting. 27018 covers public cloud PII processors only.
- Auditors assess 27018 inside an ISO 27001 audit. 27701 has its own certificate, with or without ISO 27001.
- 27018:2025 now follows ISO 27002:2022, and its new Annex B maps back to the 2019 edition.
- Annex E of 27701 maps to 27018, so one control set can serve both.
- Neither standard maps to PIPEDA, Law 25, HIPAA or the state privacy statutes. You build that map yourself.
Build one privacy program that covers both
We map your roles, build one control set that traces to ISO 27701 and ISO 27018, and prepare you for the audits. You get the certificate your buyers ask for, without running two programs.