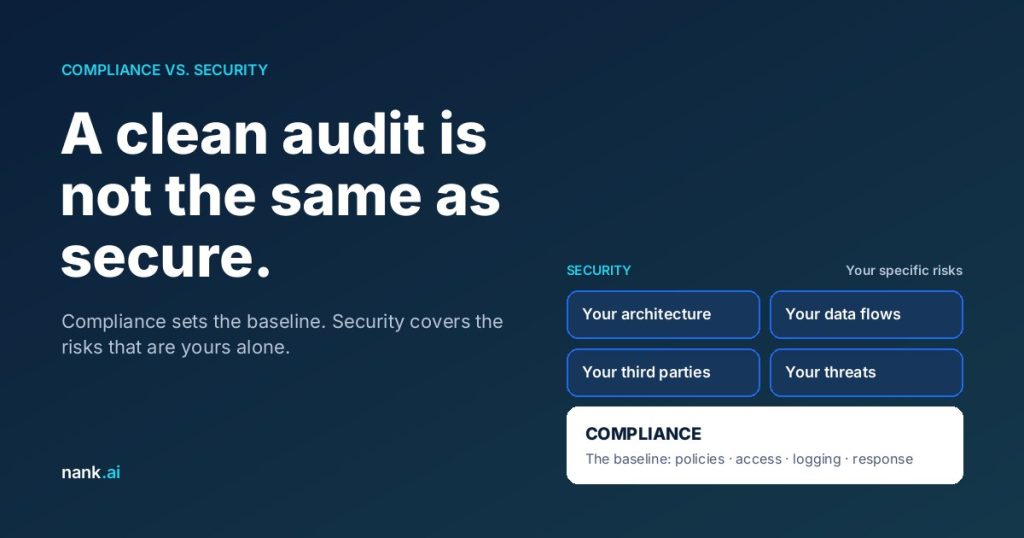
Compliance vs. Security: Why a Clean Audit Does Not Make You Secure
Compliance gives you a baseline of controls. Security covers the risks that come from your own systems, data and business. Where audits stop, and how you close the gap.


Compliance gives you a baseline of controls. Security covers the risks that come from your own systems, data and business. Where audits stop, and how you close the gap.
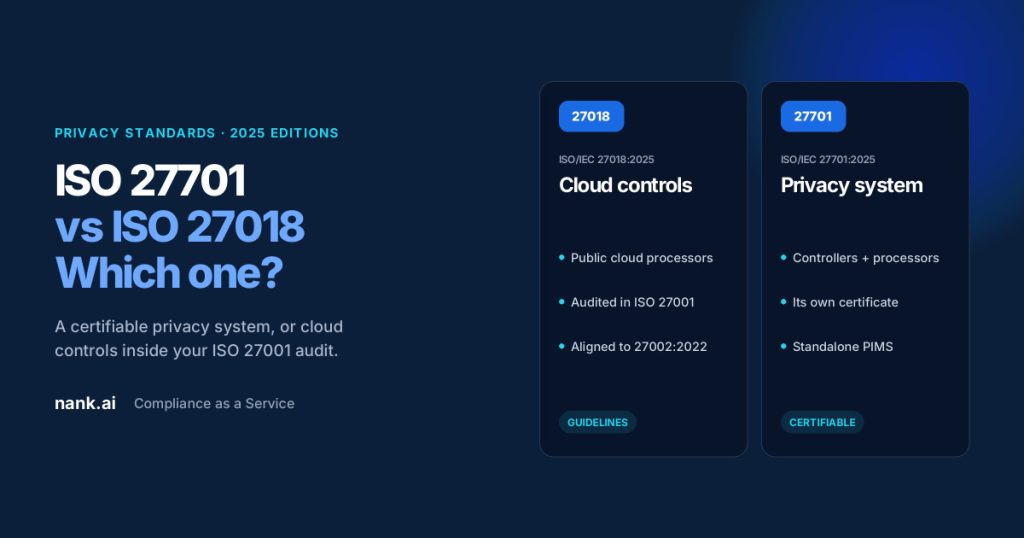
ISO 27701:2025 is a certifiable privacy management system. ISO 27018:2025 is guidance for public cloud PII processors, audited inside ISO 27001. What each covers and which you need.

Four challenges the common compliance platform creates for the teams that use it, what each one costs, and what to ask a vendor before you sign.
Compliance-as-a-Service moves most of the SOC 2 work to a platform and a named manager. Four things stay with you, and here is why.
GDPR is law and ISO 27701 is a standard you opt into. What a certificate buys you under Articles 24 and 32, and where it leaves gaps.
TL;DR Compliance automation software shows you what is wrong. It cannot write your policies, run your internal audit, or sit
Nankai is the Tianjin school founded in 1904, and we took the name for what it stood for: Gong – public spirit. Neng – ability.
How one compliance practitioner’s breaking point with GRC software became the foundation for a different kind of compliance company.
One is a certificate. The other is a report on controls you wrote. Why the overlap runs one way, and which your buyers ask for.
USD 25,000 to 80,000 in year one for most small and mid-sized companies. What drives the number, and which parts you can actually control.